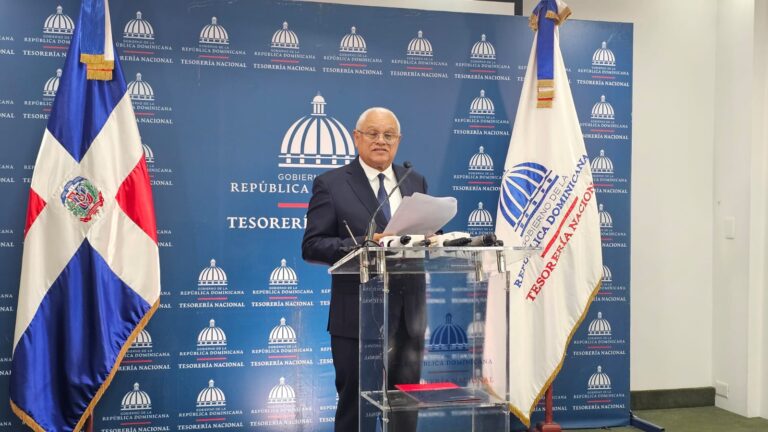

The Dominican Republic recorded 780 million cyberattacks stopped by the National Cybersecurity Center (CNCS) through October 2026, a figure that significantly exceeds the 480 million attempted attacks prevented during all of 2025, according to data provided by the entity’s executive director, Carlos Leonardo.
The official explained that the increase does not necessarily represent a proportional growth in threats, but also responds to a greater capacity for detection and monitoring, as well as the increase in digital services and connectivity in the country.
“780 million attacks stopped means that the attackers have 780 million opportunities to make a mistake; we have none”, stated Leonardo, warning that a single attack that manages to bypass protection mechanisms could lead to significant consequences.
Since the organization’s creation in 2018, the CNCS has recorded 2,035 materialized incidents, that is, those that have managed to impact systems and require the intervention of specialized teams to address their consequences.
The director pointed out that some data leaks disseminated over the last few months evidence weaknesses in the security controls of certain organizations.
Phishing, among the most frequent attacks
Among the threats identified in the Dominican cyberspace are the breaches of public institution websites, the modification of content on official portals, and the hijacking or encryption of information, which forces the affected organizations to resort to backups to recover their data.
However, the most frequent attack is phishing or impersonation of digital services, through which cybercriminals create fraudulent pages to deceive users and obtain personal information or money.
Leonardo indicated that recurring cases include fake e-Ticket portals for the General Directorate of Migration and the General Directorate of Customs, which are used to scam travelers.
The official explained that, although these fraudulent pages are identified and deactivated, those responsible for them often create new portals to continue with the operations.
However, he assured that the CNCS response time has improved. Previously, removing a fraudulent page could take between a week and a month, while currently the procedure can be completed in approximately two hours.
Protection of 326 public institutions
The National Cybersecurity Center has a national incident response team that works 24 hours a day to monitor alerts of malicious activity and protect the 326 public administration institutions.
The coverage also includes critical infrastructure related to essential services, such as electricity, drinking water, telecommunications, and digital platforms used by the public.
Leonardo described the team as the “9-1-1 for computers,” explaining that their role consists of identifying threats, alerting the affected institutions, and assisting them in responding to incidents.
The CNCS also voluntarily monitors private companies that provide essential services, with the purpose of identifying potential vulnerabilities in their systems.
Tools to prevent digital fraud
As part of its prevention actions, the agency has digital tools that allow users to verify the legitimacy of links, report scams, and check if their accounts, passwords, or IP addresses have been compromised.
The institution also offers vulnerability analysis services, incident reporting, identification of malicious links, and reporting of online child abuse content or the dissemination of intimate images.
Leonardo explained that these tools contribute to creating a database of incidents reported by citizens, which allows for the identification of recurring threats and prevents other people from becoming victims of the same scams.
In addition, the CNCS maintains a responsible vulnerability disclosure program, through which individuals with technical knowledge can report flaws detected in the State’s digital services.
Verified vulnerabilities are communicated to the corresponding institutions for their correction, while those who report them are recognized on the entity’s wall of fame.
Cyberobservatory monitors threats
The organization also has a Cyber Observatory that centralizes information on cyber-exposure indicators, vulnerabilities, and infections affecting the Dominican digital environment.
The platform uses data provided by companies and international organizations, including Fortinet, Microsoft, Cisco, and Google, to identify suspicious activities, IP addresses linked to attacks, and potentially vulnerable systems.
According to Leonardo, this tool allows for providing information on threats affecting the country and facilitating the understanding of risks present in cyberspace.
Cybersecurity as a matter of national security
The CNCS was created in 2018 through Decree 230-18, as part of the National Cybersecurity Strategy, and was subsequently transferred to the National Intelligence Directorate (DNI) through Decree 612-24, which reorganized cybersecurity competencies and created the National Cryptographic Institute.
Leonardo maintained that digital protection has acquired strategic importance due to increasing technological dependence and threats that can compromise essential services.
As an example, he recalled the cyberattack that affected the General Directorate of Budget (Digepres) in December 2020, when the institution remained for 45 days unable to carry out budget approvals, impacting the execution of resources of other public entities.
He also cited the case of Costa Rica in 2022, when cyberattacks affected government, financial, and administrative services.
The director of the CNCS differentiated the functions of that entity and the Department of Investigation of High-Tech Crimes and Offenses (Dicat), noting that the former focuses on the prevention, detection, and response to incidents, while the latter investigates those responsible and works on their prosecution together with the Public Ministry.
“Cybersecurity is a matter that concerns us all; it is not the responsibility of a single organization, it is a responsibility that begins with each individual user,” concluded Leonardo, as he called on citizens to strengthen prevention and recognize the risks that also exist in the digital environment.